Single login for multiple services
A central authentication point eliminates the need to log in separately to individual applications.


We designed and implemented a central Single Sign-On system that simplifies Medicover customers' access to multiple applications and services within a single ecosystem. The solution aggregates user data, centralizes the authentication process, and ensures secure access to subsequent applications using MFA. The system was designed as a scalable platform that can be easily integrated with further solutions operating within the organization.





Medicover is one of the most recognized healthcare companies in Poland, offering comprehensive healthcare, diagnostic services, and solutions supporting patient and employee health. With the development of digital services and growing user expectations, Medicover needed a partner to help create modern, intuitive, and scalable technology solutions — ensuring convenient access to medical services, high-quality service, and data security. That partner became Veloce.
Veloce One Id was designed as a central layer responsible for user authentication, managing user data, and handling access to integrated applications.
Veloce One Id was designed as a solution built to serve Medicover's extensive digital ecosystem. Centralizing identity reduces the number of independent login mechanisms and makes it easier to bring additional applications into a shared environment.
users in the ecosystem
central login point
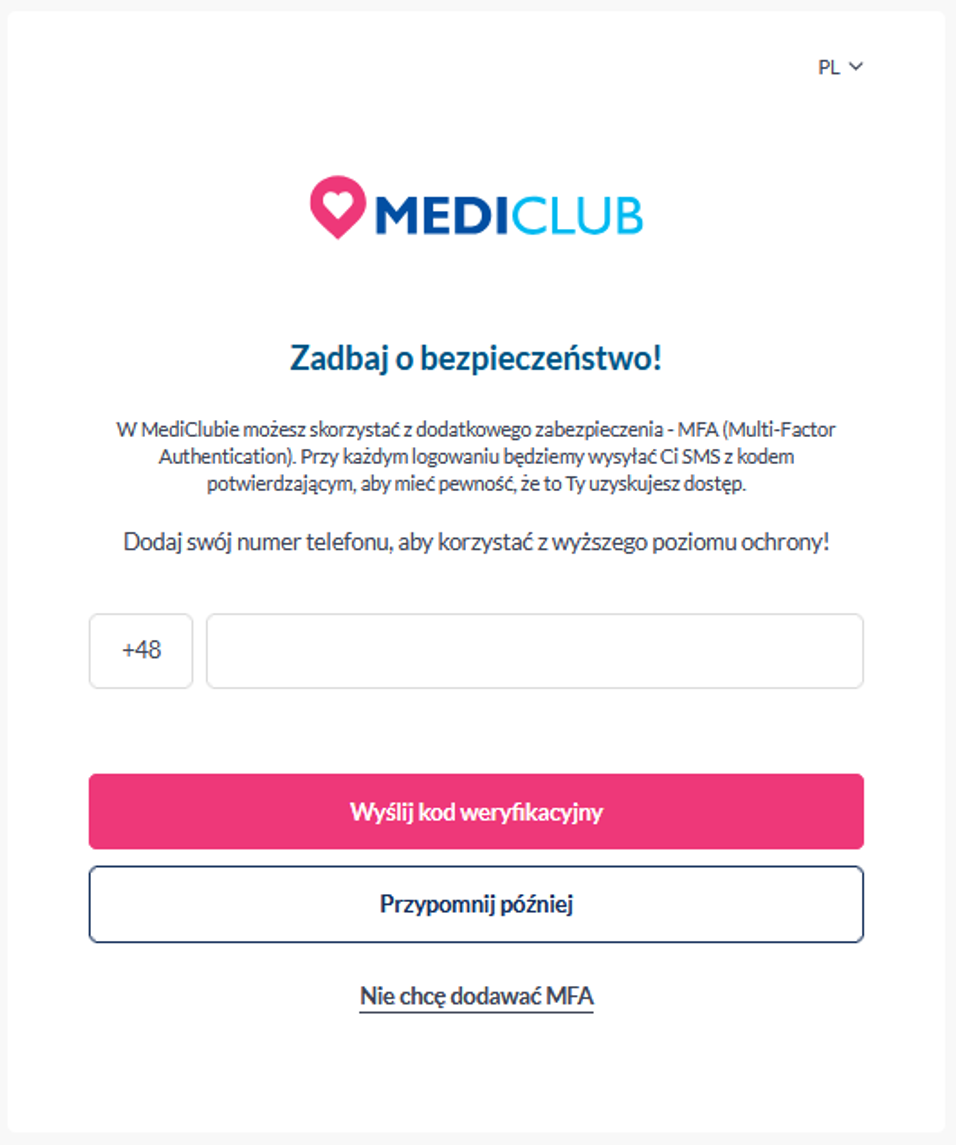
additional layer of user security
Given the system's importance to the entire Medicover ecosystem, we developed the project in stages. We worked using the Scrum methodology, delivering subsequent features iteratively and regularly verifying the solution together with the client's team.
The first step was to understand the architecture of Medicover's systems and how users interact with individual applications. We identified existing login mechanisms, user data sources, and dependencies between systems. Based on this, we defined the scope of the central SSO system and the key requirements regarding security, availability, and further development of the solution.
The next stage was designing the target architecture of Veloce One Id and the integration model with existing and future applications. We defined the approach to user identity management, the authentication process, MFA handling, and access management mechanisms. The architecture was prepared so that new applications could be easily integrated with the central system without the need to create their own login mechanisms.
We developed the system in short sprints, gradually implementing subsequent elements of the central authentication mechanism. We built a layer aggregating user data, Single Sign-On mechanisms, and MFA support. In parallel, we developed a panel enabling users to manage their own data and account settings. Each subsequent stage was tested and verified together with the Medicover team.
We placed particular emphasis on security, stability, and correct system operation across various login scenarios. We tested MFA mechanisms, authorization, session management, and integrations with client applications. We also verified the solution's performance under an increased number of simultaneous logins and the system's correct operation under heavy load.
The system was launched in the production environment and integrated with applications functioning within the Medicover ecosystem. The deployment process included configuring integrations, safely migrating users, and supporting the teams responsible for subsequent systems. Thanks to the staged approach, it was possible to limit the impact of changes on current service operations and ensure a smooth transition to the new solution.
Veloce One Id was prepared as a solution to be developed alongside the Medicover ecosystem. The central authentication layer can be used by subsequent applications, reducing the need to create independent login mechanisms and simplifying the process of deploying new services. This allows the integration of new systems to proceed faster while maintaining a consistent access model.
The growing number of Medicover's digital services meant users needed a convenient and consistent way to access multiple applications. Until now, users could encounter different login mechanisms depending on the specific system. Identity data was also scattered across individual solutions. This model increased the complexity of the environment, made it harder to manage user data, and created additional burden both for users and for the teams responsible for developing and maintaining the applications.
A central authentication point eliminates the need to log in separately to individual applications.
Simplifying access to services reduces the number of steps and lets users navigate the digital ecosystem more efficiently.
Centralizing authentication mechanisms and using MFA makes it possible to apply consistent security standards across integrated applications.
User data is aggregated in a central solution, making it easier to update, control, and keep consistent.
New systems can use the existing authentication layer instead of implementing their own login mechanisms.
Centralization reduces the number of independent authentication mechanisms requiring separate development and maintenance.
The data management panel gives users greater transparency and control over the information linked to their account.
Veloce One Id is a shared layer that can be expanded as Medicover's digital services grow.
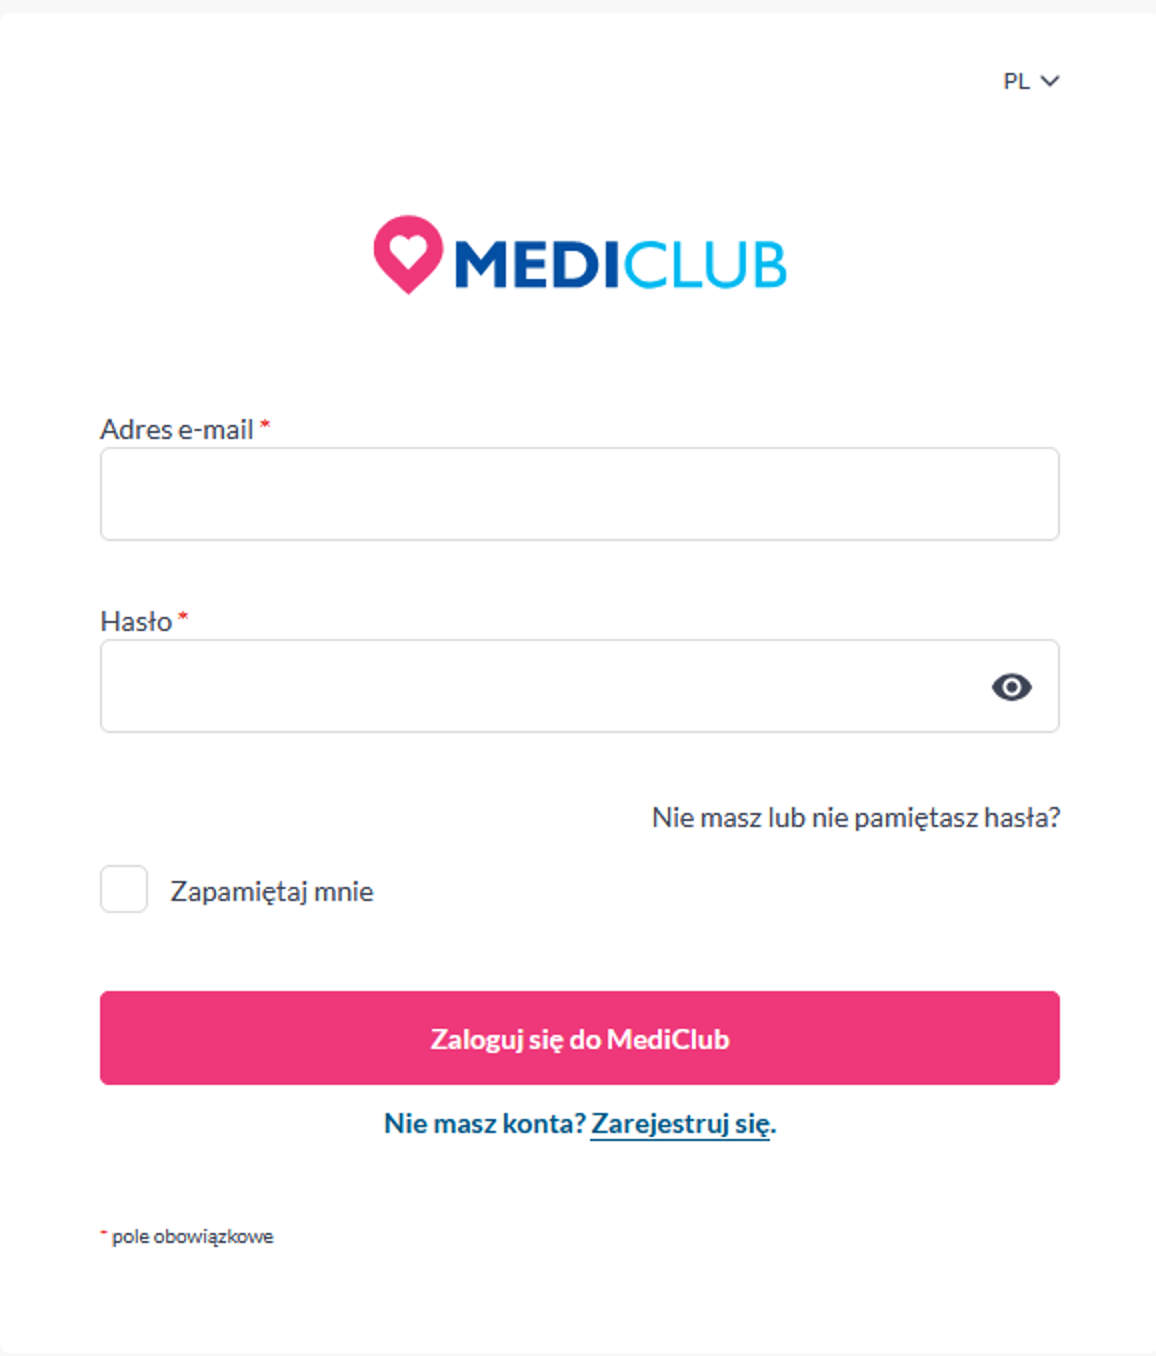
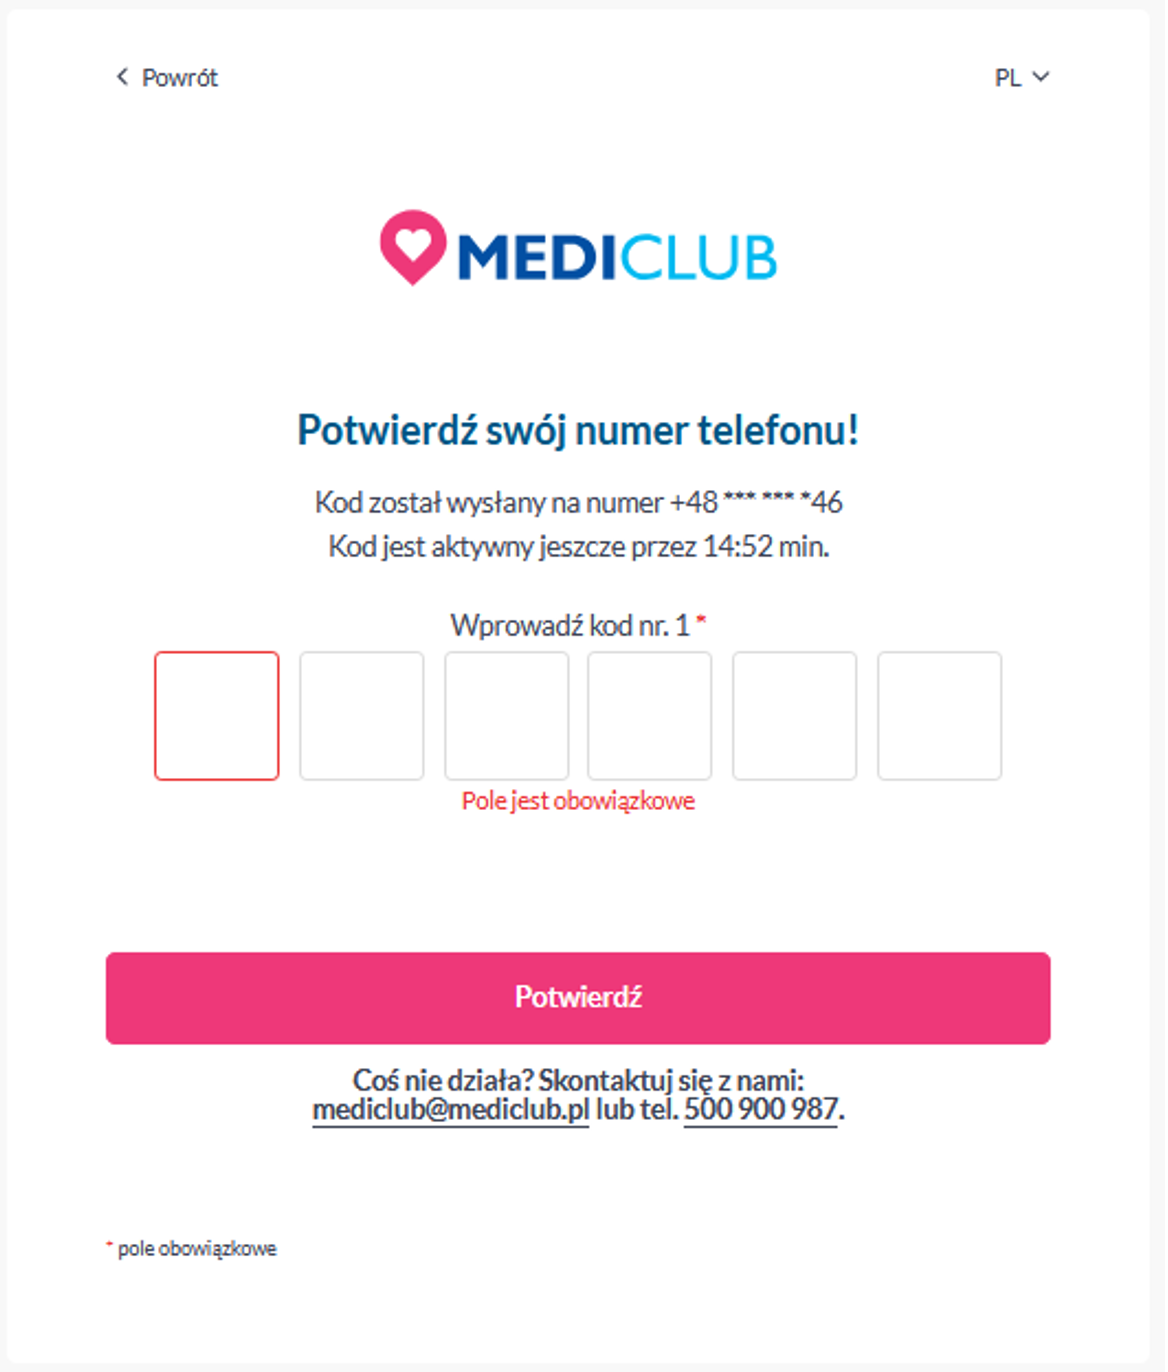
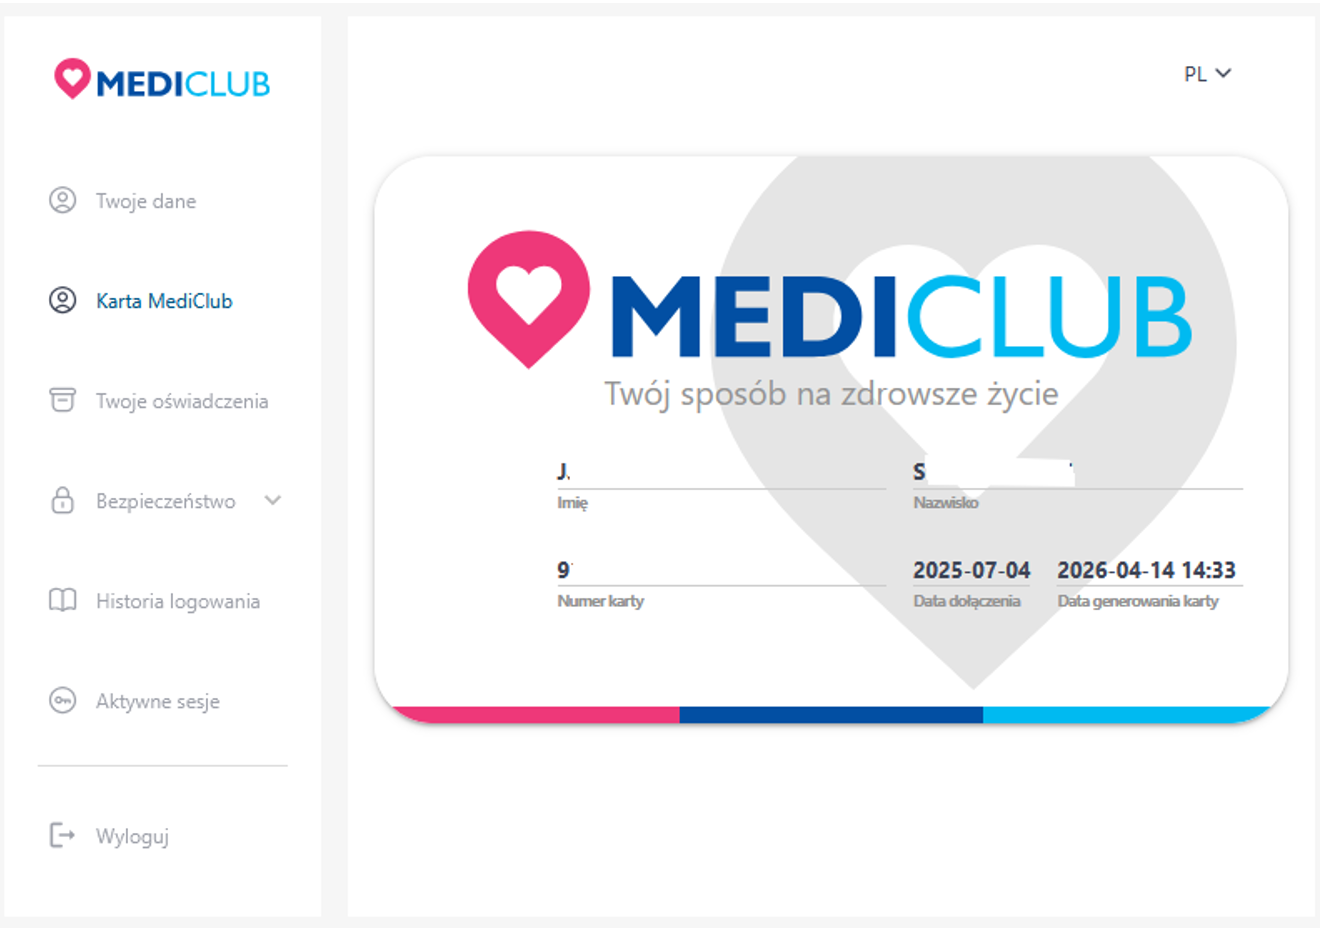
Four key screens from the user journey
" Veloce Software is one of the best, long-term suppliers supporting us technologically in developing healthcare services. Implementations are carried out with great sensitivity to the specifics of this area — they don't disrupt patient care or the functioning of facilities."
Long-term relationships with our clients are the best proof of quality and trust. We are proud of partnerships that have lasted for years — a testament to our commitment and our ability to grow alongside our clients' businesses.
Within 24 business hours we will get back to you with a proposal for an initial, no-obligation consultation. We don't sell — we advise. This is the first step to understanding whether Veloce is the right partner for your organization.